Interviews
Five questions for Kunal Miind: why hardware is the blind spot in supply chain security
The founder and CEO of Vedametric, the company behind BoardSafe, explains what hardware integrity checks involve, who is asking for them and where compliance teams should start.
By the Gazette newsroom
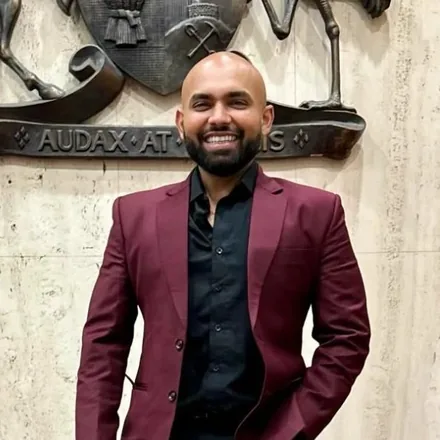
Kunal Miind is the founder and CEO of Vedametric, an Australian technology company that builds AI models, embedded hardware and secure software, and the creator of BoardSafe, a service that checks business hardware for hidden chips, counterfeit parts and altered firmware. He is an AI engineer and the author of AI System Blueprints (2022).
His work spans AI models, embedded hardware and secure software for government and defence, and he is the accountable executive for his company's published AI safety and security framework.
With supply chain risk now written into critical infrastructure rules, financial regulation and the Government's new AI safety protections, we asked him five questions about where hardware fits, who is asking for checks and what compliance teams should do first.
- Why should a CTO worry about hardware when most attacks come through software?
Because the hardware is where the software runs, and almost nobody checks it. Organisations patch, scan and test their software all the time. The phone system, the core switch and the building controller usually get plugged in on day one and trusted for ten years.
If a component has been added or swapped, or the firmware has been changed before the device reaches you, every software control sitting on top of it is working on a false assumption. The Australian Signals Directorate has said plainly that state hacking groups are already using compromised routers and smart devices as their infrastructure. That is ordinary office hardware.
- What does a BoardSafe check involve?
We come to your site. Our system compares each circuit board with the manufacturer's original design files and flags anything that should not be there or does not match, and we check the firmware against a known good version. A board takes under 60 seconds. In our internal testing we found 97% of the faults we planted.
Devices that pass get a serial-numbered, tamper-evident seal across the case join, and every inspection is recorded against that device, so you can see later whether it has been opened. Nothing leaves your premises. The design files, your data and our models all stay on site, and our models are our own, so nothing is sent to an outside AI service.
- Who is asking for it?
Two groups, and they are often on opposite sides of the same contract. Critical infrastructure operators, banks and government agencies need evidence for their risk programs. Then there are the vendors and integrators who sell to them.
More and more it is the supplier who calls first, because they know the question is coming in the tender. We ran our first trials with two Australian defence contractors before launch, and the interest since then has followed the same pattern: the people who will be asked for proof want to have it ready before they are asked.
- How does this fit with SOCI, CPS 230 and the new AI rules?
None of those rules tells you to open up a router. What they do is make you responsible for risks in your supply chain and ask you to show your work. The SOCI risk management program rules cover supply chain hazards. CPS 230 makes regulated financial entities manage the risk from their material service providers. The AI safety protections the Government announced this month add rapid incident reporting.
A per-device inspection record is one piece of evidence you can put in front of an auditor or a regulator for the hardware part of that picture. It is not a certification, and we are careful never to call it one.
- Where should a compliance or technology lead start?
Start with a list. Write down every device that handles your calls, your data or your buildings: phone systems, servers, core network gear, firewalls, printers, building and plant controllers. Rank them by what someone could do if they controlled that device.
Then ask your suppliers what evidence they can give you about where the hardware came from and whether it has been opened. If the answer is nothing, check a sample of the highest-risk devices first. You do not need to check everything on day one to know far more than you do today.
Background: what the rules say
The risk management program rules under the Security of Critical Infrastructure Act require responsible entities to identify and, as far as reasonably practicable, minimise material risks from supply chain hazards. APRA's CPS 230, in force since 1 July 2025, requires banks, insurers and superannuation trustees to manage the risks from their material service providers. On 10 November 2026 the Prime Minister announced mandatory AI safety and security protections, including incident notification and a new regulator, to be legislated through Australian AI Standards.
BoardSafe is available to government, defence, critical infrastructure and enterprise customers, priced per device. Details are at boardsafe.com.au. Answers have been edited for length.